Claude uncovered 38,000 vulnerabilities, yet shockingly, it only finds them and never patches a single one.
Recently, the practice of AI bug hunting has become extremely polarized.
On one side, AI can trace back all historical issues in one go: it first unearthed a major underlying security vulnerability in PHP, then found 948 Linux kernel vulnerabilities...
On the other side, the open-source community is almost driven to collapse: you've found the vulnerabilities, why don't you fix them already!
Yesterday, cybersecurity firm VulnCheck released a performance report on Anthropic's Project Glasswing.
It shows that seven months after the launch of Project Glasswing, Claude has cumulatively identified 37966 candidate vulnerabilities.
But as of now, only 217 of them have been fixed in public records.
VulnCheck couldn't help but question: has the once highly anticipated "Mythos Era" of cybersecurity really arrived?
38000 Vulnerabilities: How Many Have Actually Been Fixed?
First, let's recap the "Project Glasswing" that Anthropic grandly announced and launched in April this year.
The project aims to use Claude to conduct large-scale security vulnerability mining in critical software and open-source projects, cooperate with technology enterprises and open-source maintainers to promote vulnerability fixes, and eliminate security risks before they are exploited.
The name of the project has two implications.
For one thing, security vulnerabilities, just like glasswing butterflies, hide in plain sight and remain undiscovered for decades; for another, transparency itself is a form of protection. Anthropic hopes to achieve better protection for software systems through more transparent security research and vulnerability disclosure mechanisms.
Glasswing butterfly, scientific name Greta oto | Source: Wikipedia
At the initial launch, Anthropic claimed it would provide 100 million US dollars in model usage credits and 4 million US dollars in open-source security donations, and also announced that its ace cybersecurity model Claude Mythos Preview had discovered thousands of high-risk and critical vulnerabilities. Soon after, Apple, Google, Microsoft, AWS, NVIDIA and many other players joined the initiative one after another.
But is that really the case?
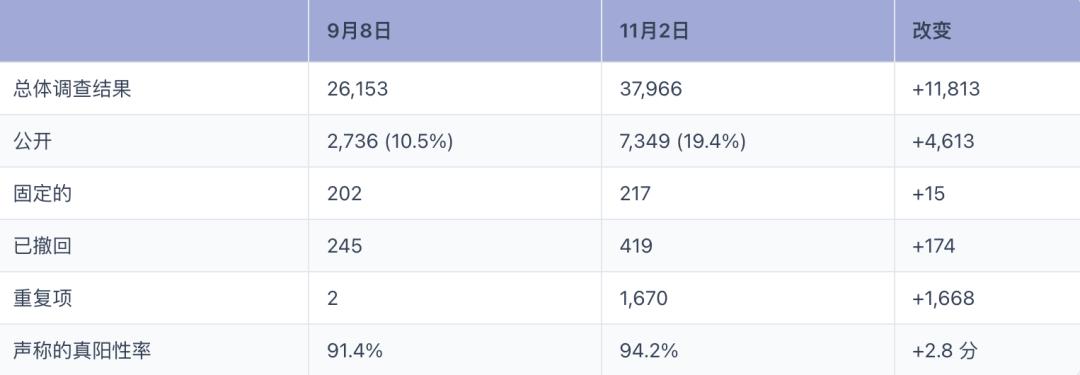
According to the continuously tracked data from VulnCheck, as of the beginning of November, Anthropic's candidate findings have reached 37966, but only 217 are marked as fixed in the vulnerability disclosure ledger.
Meanwhile, invalid data is still accumulating: there are 419 vulnerability withdrawal entries, and the number of duplicate entries is as high as 1654.
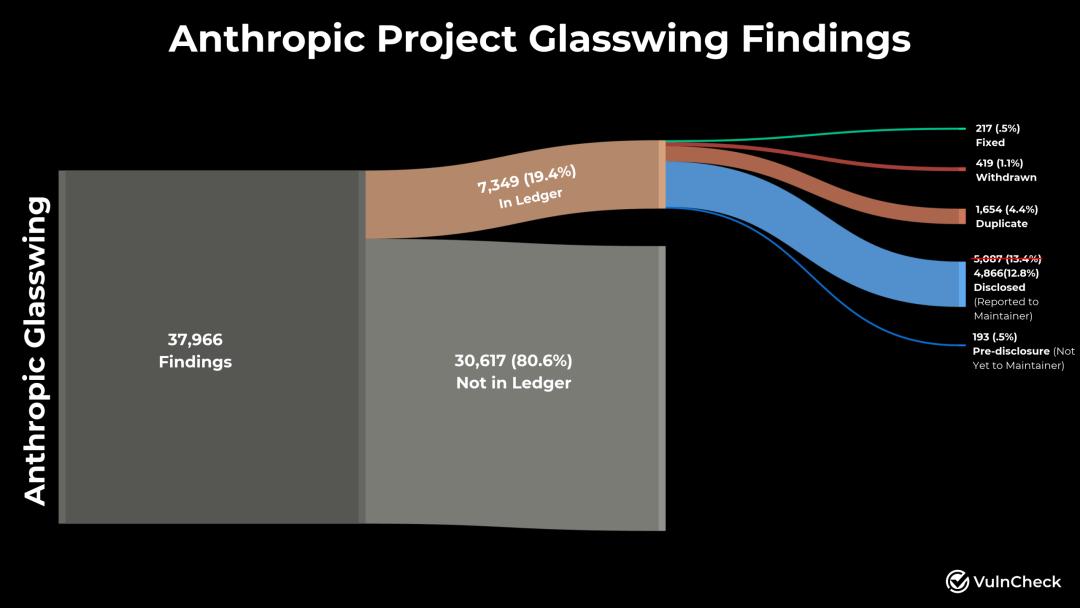
Source: VulnCheck
This gap is still widening at an accelerating pace.
In just the past two months, the number of candidate vulnerabilities has surged by nearly 12000, but the number of fixed records has only increased by a mere 15.
In addition, the 442 CVEs attributed to Anthropic tracked by VulnCheck only account for 0.5% of the total number of public CVEs worldwide in 2026.
△ Source: VulnCheck
According to the data disclosed by Anthropic, as of November 2, among the 37966 candidate findings, 6376 have been reviewed by external security experts, 6009 findings are valid, 5087 of which have been reported to software maintainers, and 629 have obtained upstream patches.
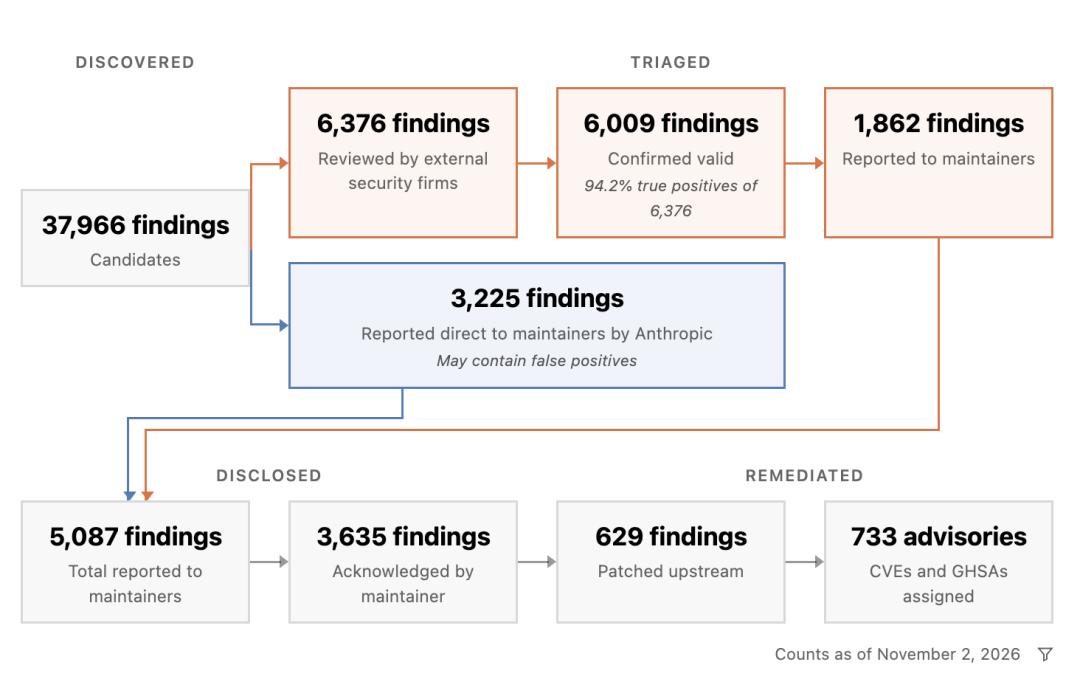
Although there is a slight difference in the number of fixes due to different data calibers, both sides have found one thing in common.
That is, with the intensity of AI vulnerability mining, manual review is completely unable to keep up.
Anthropic has long realized this point, and the official also admitted that the serious bottleneck of manual verification capacity has greatly limited the efficiency of vulnerability review and disclosure.
Therefore, on October 8, it launched a service called OSS Scanner.
Open-source project maintainers can sign up voluntarily to let Claude scan their code for free, so that the vulnerability report generated by the model can be sent directly to the maintainers, without waiting for Anthropic to organize manual review.
Open-source Maintainers Cannot Keep Up With Fixes
AI is forcing us to immediately pay off 40 years of accumulated technical debt.
Behind this data gap, the most affected parties are open-source maintainers. For example, VulnCheck cited the case of curl, a network data transmission tool.
At the beginning of November, curl maintainer Daniel Stenberg received another big package from Anthropic, containing 45 vulnerability reports.
Long before that, Daniel wrote in his blog that core maintainers have been overwhelmed by the continuous influx of reports.
We aim to not drown.
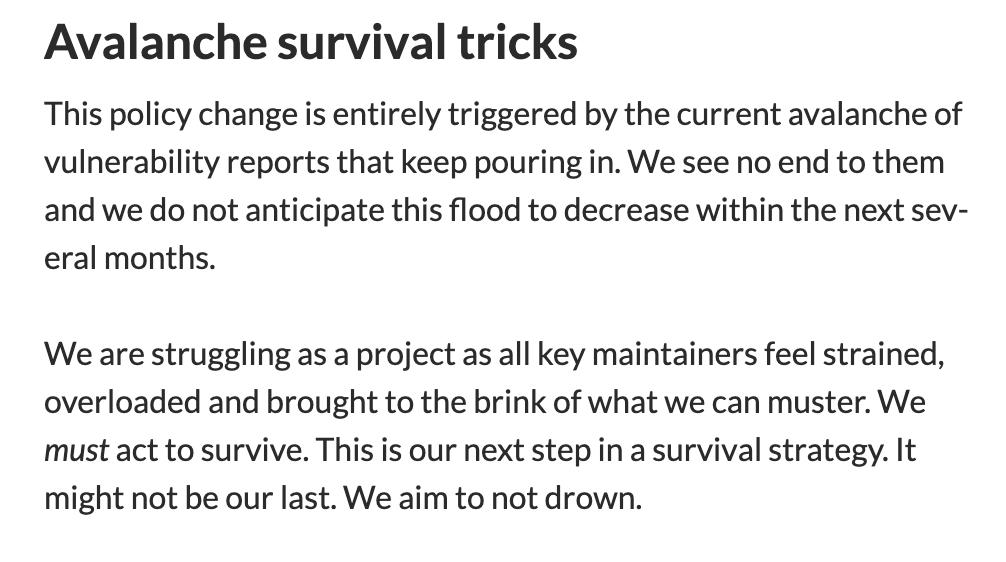
To cope with so many reports, Daniel announced to modify curl's security vulnerability handling rules. Low-risk and medium-risk vulnerabilities will be changed to be discussed publicly on GitHub, so that more community developers can help with the review.
At present, among the 34 public reports of curl, 19 have been judged not to constitute security vulnerabilities, and 6 have been confirmed as low-risk vulnerabilities.
VulnCheck's report implicitly points out that it was previously claimed that all these vulnerabilities are of serious harm, but now it seems that Project Glasswing is hardly useful except for adding extra review workload to people?
In fact, Anthropic did once dig out a critical vulnerability for curl.
In September this year, Anthropic used Claude to discover a Use-After-Free memory error in curl. When specific conditions are met, a malicious server may even use this flaw to achieve remote code execution.
Daniel said it is one of the most serious vulnerabilities of curl over the years.
So to sum up, VulnCheck's report is actually very similar to an advertisement for its own business, because the problems of Project Glasswing it criticizes happen to highly match the vulnerability intelligence and priority management services provided by itself...
One More Thing
At this point, some people may wonder, since Claude is so powerful, why not fix the problems directly when it finds them?
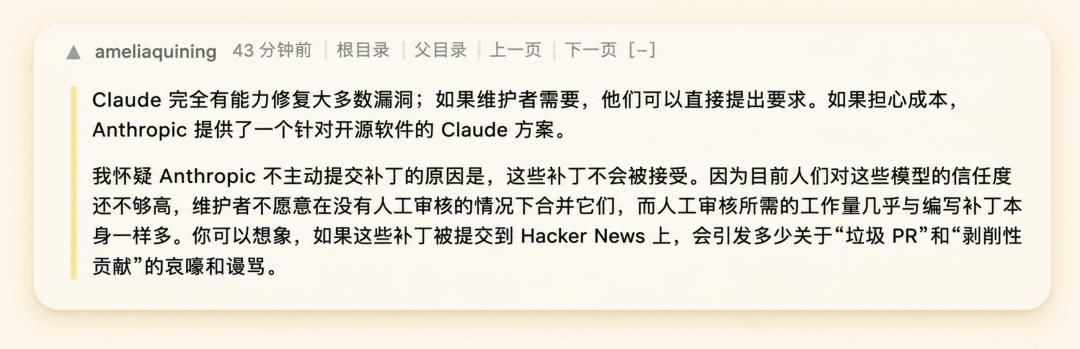
In fact, Anthropic has already made AI generate candidate patches.
However, developers have long suffered from AI-generated bug fixes... "It is indeed not difficult for LLM to generate repair procedures, the hard part is whether open-source projects are willing to adopt them."
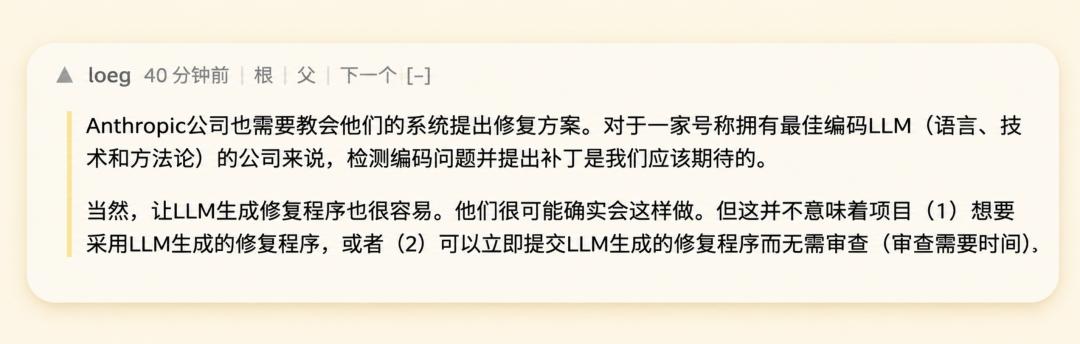
The workload of reviewing an AI-generated patch is sometimes almost equivalent to rewriting the code by yourself.
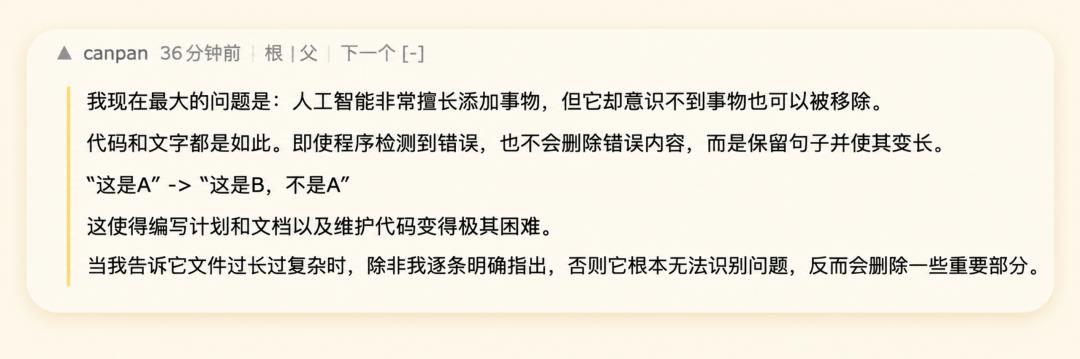
It is often the case that "lighting a candle only illuminates more darkness": when AI starts fixing a problem, it adds more complex logic to the code for the purpose of repair, and finally after fixing one bug, it brings ten new problems.
"AI is very good at adding things, but it doesn't realize that things can also be removed..."
So at least for now, the pits dug by these most powerful models still need humans to fill.
References:
https://www.vulncheck.com/blog/anthropic-glasswing-november-update
This article is from WeChat Official Account "QbitAI", author: Cheng Qian, published by 36Kr with authorization.