Anthropic has not released its model, yet it has discovered a system-level fatal vulnerability in Linux.
AI has once again triggered a massive cybersecurity earthquake!
It is reported that a near-perfect Linux kernel vulnerability in Ubuntu and Red Hat systems remains unpatched to this day.
Even more chilling, a cutting-edge large model that Anthropic has not yet released has successfully converted this originally theoretical-level vulnerability into a high-risk exploit chain that can remotely obtain root privileges!
Imagine this: your server runs silently on the internet, with no password, no interaction, and no need for the user to click a mouse. A stranger sends several sets of carefully constructed TCP packets, and after more than half an hour, the attacker can execute arbitrary commands on your machine with root privileges.
Now the logic of cybersecurity defense has completely collapsed — what AI has changed is not the number of vulnerabilities, but the speed of weaponizing vulnerabilities, which has been forcibly compressed from "several months" to "several hours".
When AI incarnates as a tireless "super hacker", is our digital world still safe?
Full-score meat grinder: How terrifying is CVE-2026-98432?
In the cybersecurity industry, the full score of CVSS (Common Vulnerability Scoring System) is 10 points.
Any vulnerability with a score higher than 9 points is enough to make security operation and maintenance personnel of major global companies wake up from bed in the middle of the night and rush to work overtime to patch it.
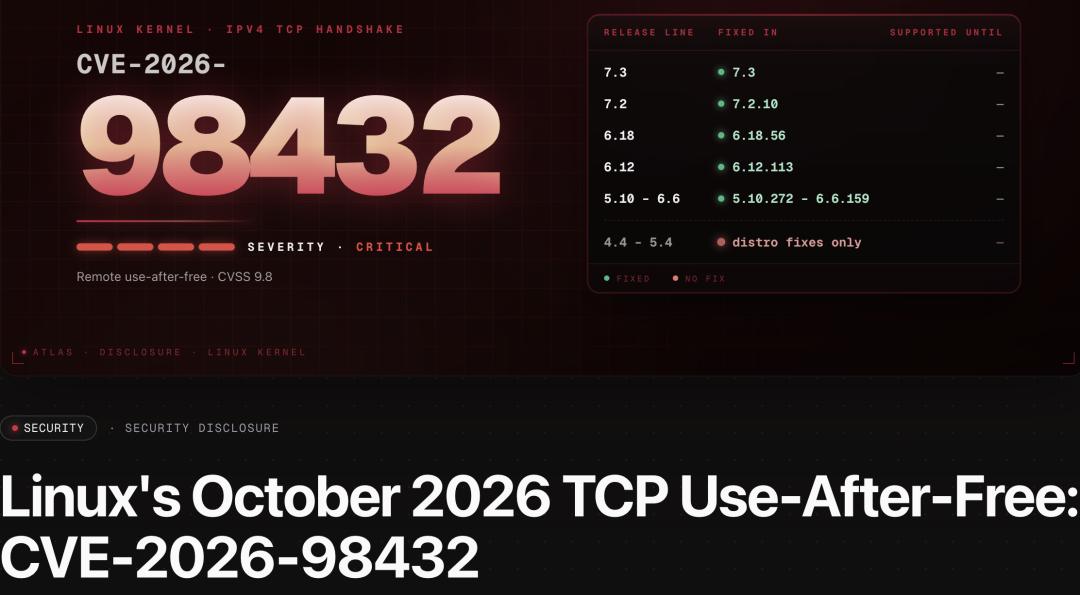
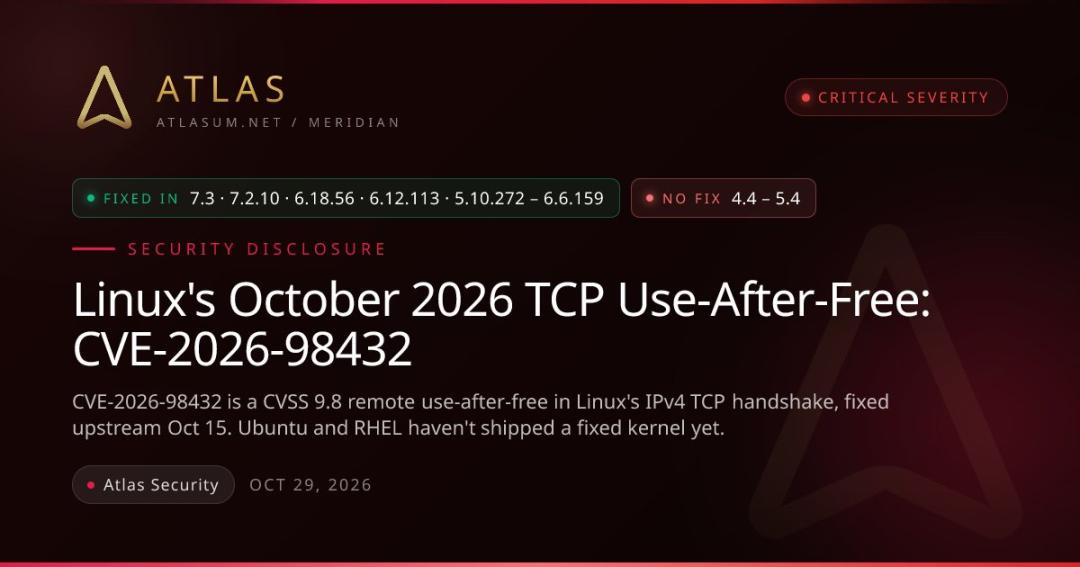
And the protagonist this time, CVE-2026-98432, has a score as high as 9.8 points.
It is network-accessible, requires no authentication, no user interaction, and has high confidentiality/integrity/availability impact. It has existed since Linux 4.4, covering almost all mainstream server kernels in the past decade.
This is a Use-After-Free (UAF for short) vulnerability that exists in the IPv4 TCP handshake process.
Simply put, when the kernel creates a new connection, it directly transfers the IP option memory from the request socket to the new socket, but releases it without properly waiting for all CPUs to finish reading.
Another CPU is still using this piece of memory to send SYN-ACK, and as a result, it accesses the already released memory.
For example:
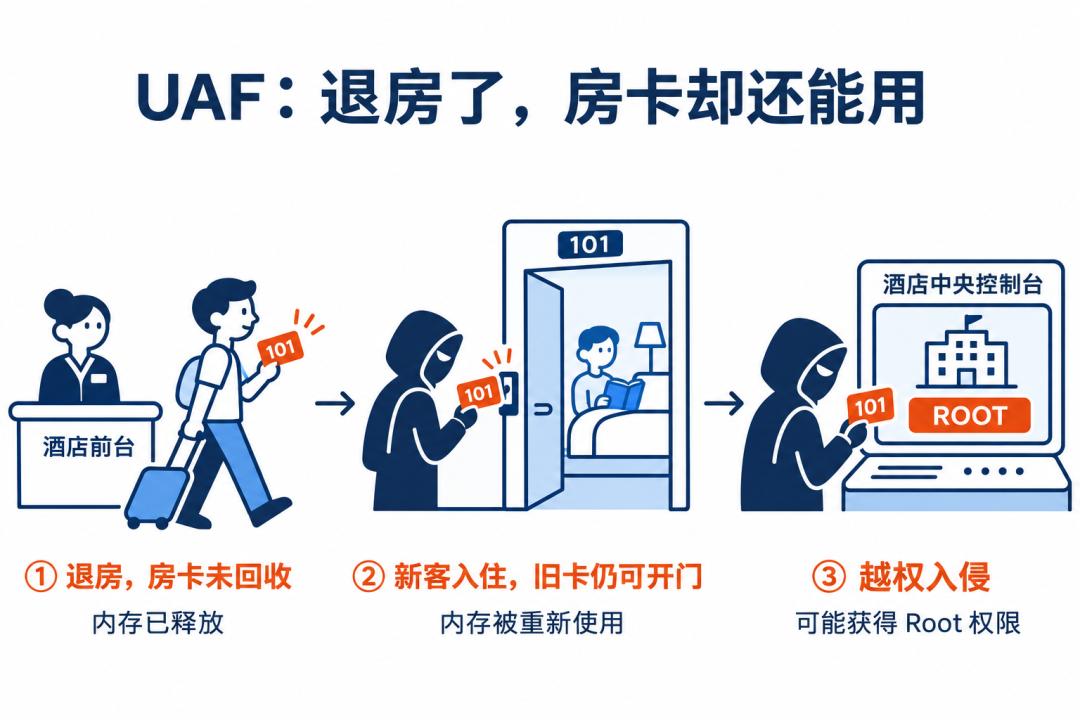
Assume that the server is a hotel, and the IPv4 TCP handshake is the process where a guest (data packet) goes to the front desk to check in for a room.
The UAF vulnerability is equivalent to: a guest checks out (the memory is released), but due to some logical error, the system does not take back the room card in his hand.
When the next innocent guest (or core system program) moves into this room, the hacker holding the "expired room card" can swagger in and even directly take over the control of the entire hotel (that is, obtain root privileges).
The most fatal point is that triggering this vulnerability "does not require any credentials".
Hackers do not need to know your account, do not need to know your password, and do not even need you to run complex high-risk services on the server.
No phishing, no user clicking links, no existing privileges required. As long as your machine exposes the IPv4 TCP service to the outside world (almost all public network servers do), it may theoretically be compromised. If the Network Load Balancer of cloud vendors transparently transmits IP options, the target machines behind it will also be affected.
Because the vulnerability exists in the lowest-level IPv4 TCP handshake — as long as your server is still connected to the network and receiving network requests, you are under the gun.
The most dangerous point is that a failed race condition only causes the handshake to fail, and the system will not crash. Attackers can retry infinitely until they succeed.
In Anthropic's experiment, it took about 48 minutes to leak the kernel pointer (bypassing KASLR), and another 5 minutes to get the root shell. The whole process took about 53 minutes.
Anthropic explicitly stated that the experiment targeted servers with Multipath TCP (MPTCP) listening enabled. For Go 1.24 and later versions, MPTCP is enabled by default for listening sockets on Linux.
Countless Go-written microservices, API gateways, and cloud-native services may be quietly opening this backdoor.
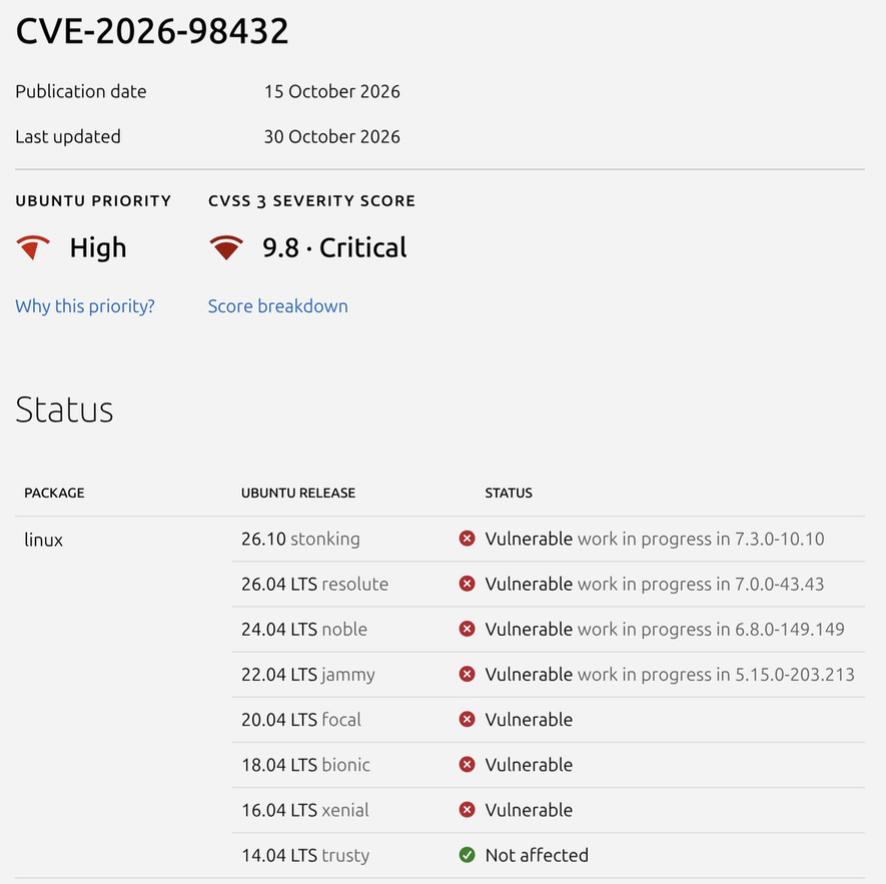
At present, Ubuntu and Red Hat (RHEL), the two operating systems that occupy half of the enterprise market, still have not released official patches to fix this kernel vulnerability!
This means that millions or even tens of millions of servers around the world are in a completely unprotected "naked running" state.
Faced with a 9.8-point low-level vulnerability, any "folk remedies" are self-deception.
At present, only a few distributions such as Debian, Amazon Linux and Oracle UEK have truly fixed this problem at the kernel level.
The majority of Ubuntu and RHEL users are sitting on a powder keg with a lit fuse.
AI did not "discover" the vulnerability, but what it did is even more terrifying
The real core of this crisis is not that AI discovered another vulnerability, but that AI has completely subverted the industry —
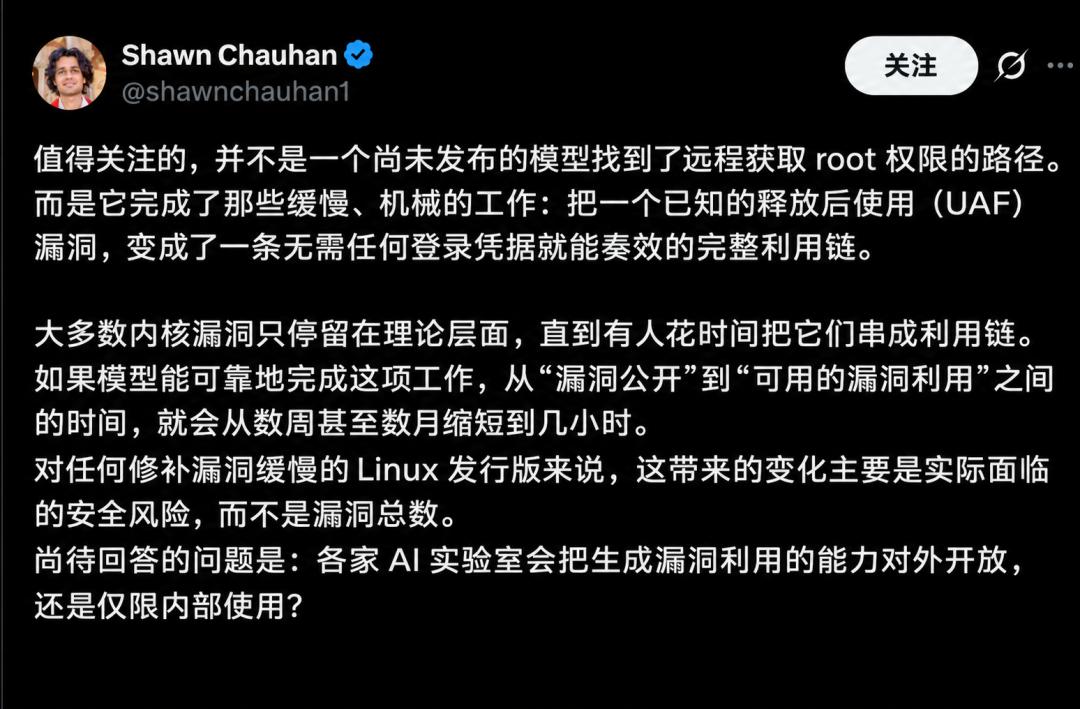
The interesting part is not that an unreleased model found a remote root path. Instead, the model completed the slow, mechanical work: converting a known use-after-free into an exploit chain that works without credentials.
For a long time, there has been a subtle "time difference umbrella" in the cybersecurity industry.
When an extremely complex kernel vulnerability is made public, it is usually only a proof of concept, or only stays at the theoretical level. Why?
Because turning a low-level memory vulnerability into a 100% usable exploit chain is extremely slow, extremely testing the patience of hackers, and it is a "mechanical craft work".
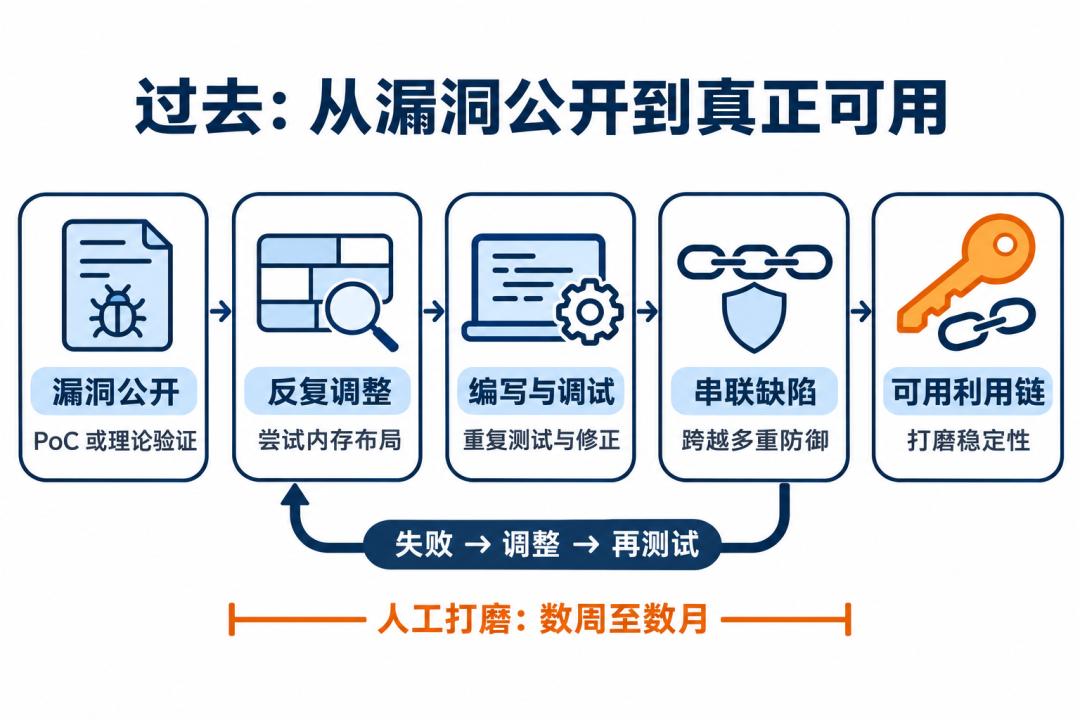
To polish a truly usable "key", top hackers may spend weeks or even months, constantly trying the layout of the memory space, writing tedious code, and connecting multiple tiny logical defects.
It is this "weeks to months" time difference that gives major global software vendors time to develop patches, and also gives system administrators time to update their systems.
However, Anthropic's unreleased AI model has personally crushed this umbrella.
What is AI best at? It is tirelessly and extremely accurately processing those slow, complex mechanical logical deductions that require huge workloads.
This unreleased AI model from Anthropic is a "monster" that has both the intuition of top human hackers and the computing power and patience of a machine.
When the theoretical vulnerability of CVE-2026-98432 is placed in front of it, it can automatically deduce tens of millions of memory states in a very short time, and piece those scattered theoretical fragments into a sharp blade that directly stabs the heart of the server!
Anthropic only disclosed the results this time and did not make the exploit code public. But once similar capabilities spread, the time from "discovery" to "weaponization" of vulnerabilities will be drastically shortened.
"If the model can reliably do this work, the window from 'public vulnerability' to 'usable vulnerability exploit' will be shortened from weeks or months to hours."
This is the most chilling part of this incident! What it changes is not the absolute number of vulnerabilities in the cyber world, but cruelly changes the "actual security posture" of the defending side.
In the past, when system administrators saw a vulnerability announcement, they could drink a cup of tea and schedule it into the update plan for the next month; now, a few hours after the vulnerability announcement is released, the automated attack weapons fully generated by AI may have already flooded the dark web.
How can the physical operation and maintenance speed of humans compete with the code generation speed of AI?
We are being forced into a "dimensionality reduction strike"
Daron Acemoglu, Nobel laureate in economics, once warned:
AI may reduce ordinary workers to second-class citizens.
In the field of cybersecurity, this kind of dimensionality reduction strike has already staged in advance. Without mastering top AI defense tools, traditional security engineers are being reduced to "second-class citizens" on the cyber battlefield.
In the past, only state-level advanced persistent threat organizations had the financial and human resources to weaponize complex 0day or Nday vulnerabilities. Therefore, the probability of ordinary enterprises being attacked by such advanced exploit chains was not high.
But now, AI is making the ability to "manufacture top cyber weapons" equalized, cheap, and instantaneous.
Just imagine, once the capabilities similar to Anthropic's cutting-edge model leak out, or are reverse-engineered and implemented by hacker organizations, what will happen?
A junior script kiddie only needs to enter a prompt: "Help me write a remote root attack script for the Linux CVE vulnerability that was just exposed yesterday", and AI can generate a set of highly lethal code in a few minutes.
The defending side is still slowly going through the process, testing compatibility, and waiting for the vendor to release patches; the attacking side's "AI arsenal" has mass-produced the latest missiles and poured them down.
How to fight this asymmetric war?
The wheels of the AI era are crushing all old rules. In this cybersecurity dimensionality reduction strike set off by large models, no one can stay out of it.
We either learn to build a new generation of automated defense systems at the "minute level" or even "second level" with the assistance of AI, or we can only watch the digital buildings we built on the Internet be blown to pieces by the artillery fire generated by AI.
Who is the most dangerous in the real world?
Current public intelligence shows that there is no confirmed report of large-scale wild exploitation, but scanning activities have already appeared. Security personnel have observed a significant increase in detection traffic targeting MPTCP ports. Once the vulnerability window is truly weaponized, the consequences will be unimaginable.
What can we do right now?
1. Prioritize patching and restart Red Hat/AlmaLinux/Rocky: install the kernel package released in early November as soon as possible and reboot; Debian/Amazon Linux: update directly and restart; Ubuntu: pay attention to the official security announcement and -proposed, and deploy it as soon as possible after the official release.
2. Temporary mitigation if MPTCP is not needed: sysctl -w net.mptcp.enabled=0. Use nftables/iptables to filter TCP packets with abnormal IP options, and strictly restrict source IP for services that do not need public network access.
3. Inventory assets: immediately scan (uname -r), check if there is MPTCP listening (ss -tlnp | grep mptcp), and which machines are running Go 1.24+ services.
The patches are already available, but some distributions are still in the process of rolling out. This is not the time to wait and see, it is time to act. Go check your servers now. Don't wait for others to "check" for you.
There is not much time left for humans to patch.
References:
https://x.com/shawnchauhan1/status/2117134617769898241
https://atlasum.net/blog/cve-2026-98432-linux-ipv4-tcp-uaf
This article is from the WeChat official account "AI Era Insights", author: ASI Revelation, editor: David Aeneas, published with authorization from 36Kr.