A major critical security flaw has been exposed in PHP, programmers around the world are staying up late to work overtime, and this super severe vulnerability was discovered by ChatGPT.
Catastrophic trouble everyone, the best programming language PHP has suffered a critical security breach!
Two extremely high-risk vulnerabilities have just been exposed, with their severity scores both reaching the highest priority range of 9.2 points.
In the worst-case scenario, attackers can execute code on the server without logging in. Almost all versions starting from PHP 5.4 are affected, including a large number of still widely used 7.x and 8.0/8.1 versions.
The official team has explicitly stated that there are no complete mitigation measures, and the only safe practice is to upgrade immediately.
The key problem is that the official team has long stopped supporting PHP 8.1 and earlier versions, so there is no patch available at all!
It is well known that PHP powers 70% of websites around the world. According to Reuters, some government websites in the Netherlands, Finland and other regions have already taken offline in advance to defend against potential incoming attacks.
Teams in Japan are also working overtime through the night... (You know what the situation of Japanese websites is like)
Amid all the chaos, guess what happened?
Hey, OpenAI has done it again:
It turns out that these two vulnerabilities, collectively referred to as PHP2Shell, were first discovered by GPT-5.6 Sol.
OpenAI's official statement reads as follows:
The security firm Calif used GPT-5.6 Sol to discover critical vulnerabilities in PHP. Wiz also independently discovered and reported these two vulnerabilities.
OpenAI also played a leading role in the subsequent patch update process.
After this post was released, the reactions of the public were like:
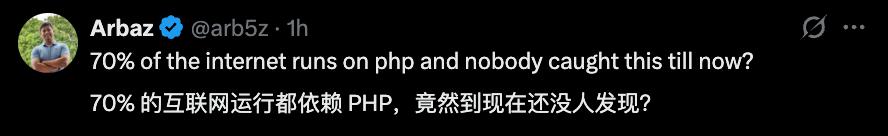
AI is really the ultimate game-changer?!
Also, here is the key point to note. OpenAI's announcement states that this major PHP security incident is "only part of the numerous critical vulnerabilities we have discovered and are working to fix".
OpenAI estimates that the number of similar vulnerabilities will increase sharply in the coming months...
GPT Discovers Super Critical Vulnerabilities
Before diving into the details of this incident, here is a reminder for everyone.
The two vulnerabilities are numbered CVE-2026-109618 and CVE-2026-109619 respectively.
CVE-2026-109618: It leads to incomplete internal data structures through out-of-memory (OOM) errors, and invalid data is processed as valid data during request cleanup, which can result in memory corruption and RCE (Remote Code Execution).
CVE-2026-109619: The global state related to requests remains after the memory is freed, and subsequent requests processed by the same worker will access the freed memory (use-after-free), which can also lead to RCE.
The officially released patched versions include:
PHP 8.5.12, PHP 8.4.27, PHP 8.3.36 and PHP 8.2.35.
All PHP deployment environments that handle web requests, including PHP-FPM, Apache with mod_php module, php-cgi, FrankenPHP and LiteSpeed, are at risk. Among them, mod_php has the highest risk level.
Researchers have successfully reproduced unauthenticated remote code execution on some deployed WordPress, Drupal and Joomla sites.
So how did GPT-5.6 Sol discover these two vulnerabilities?
OpenAI launched an open source security initiative called "Patch the Planet" in June 2026.
The core goal of this program is to use AI to help discover vulnerabilities in open source projects, while solving new problems brought by AI: models can discover a large number of vulnerabilities, but open source maintainers are severely understaffed and easily overwhelmed by massive reports. Therefore, AI should not only find bugs, but also debug them.
The security firm Calif is one of OpenAI's initiative partners. It was under the Patch the Planet framework that Calif discovered one of the key issues in this major PHP vulnerability incident.
At the same time, another well-known security company Wiz Research also independently discovered and reported the related vulnerabilities. Wiz also used AI in the research process, including Wiz Atlas, Gemini 4 Argon and GPT-5.6 Sol. Among them, Gemini 4 Argon played an "indispensable role" in vulnerability discovery, exploit development, attack detection and patch verification.
Over the past two months, OpenAI has taken the lead in coordination, working with PHP maintainers, Wiz, Cloudflare and other parties to prepare patches and mitigation measures, and has just publicly announced and released the patched versions.
(The long time spent is mainly because the fix involves the underlying PHP engine, with relatively large code changes.)
In OpenAI's own words, this time, cutting-edge AI has opened a "defender's window" for maintainers and security vendors before attackers can take action.
It is worth noting that OpenAI reminds that the impact of this batch of vulnerabilities is significant, but this is only the beginning...
They are only part of the numerous critical vulnerabilities we have discovered and are working to fix. The number of similar vulnerabilities will increase sharply in the coming months.
As Wiz pointed out, AI lowers the threshold for exploiting complex vulnerabilities, and can also help the defending side discover and fix vulnerabilities.
A new form of AI competition in the AI era has officially kicked off...
For the full vulnerability reports, please refer to the PHP announcement and Wiz report:
PHP Security Advisory: https://www.php.net/index.php#2026-10-21-5
Wiz Report: https://www.wiz.io/blog/php2shell-php-rce
Reference Link: https://openai.com/index/coordinated-disclosure-of-critical-vulnerabilities/
This article is from the WeChat official account QbitAI, written by Yu Yang, and published with authorization from 36Kr.