"Jinghua Secret Computing" completes a nearly RMB 100 million Pre-A round of financing, fully solving the dilemma that "AI cannot be safely applied" in high-sensitivity scenarios | Lighthouse Capital Portfolio
A technology enterprise "Jinghua Privacy Computing" focused on AI privacy-preserving computing, officially announced today that it has completed Pre-A round of financing. This round of financing is jointly led by Zhongguancun Science City and Northern Venture Capital, with joint investment from Huacang Capital and Ultimate Investment, and continued additional investment from existing shareholders Inno Tech Fund and SJ Capital.
Jinghua Privacy Computing has successively completed three rounds of financing within half a year. The financing amount of this round is nearly 100 million yuan, and the funds will be mainly invested in in-depth adaptation of domestic computing power, iteration of underlying privacy-preserving computing technology and R&D of dedicated privacy-preserving chips.
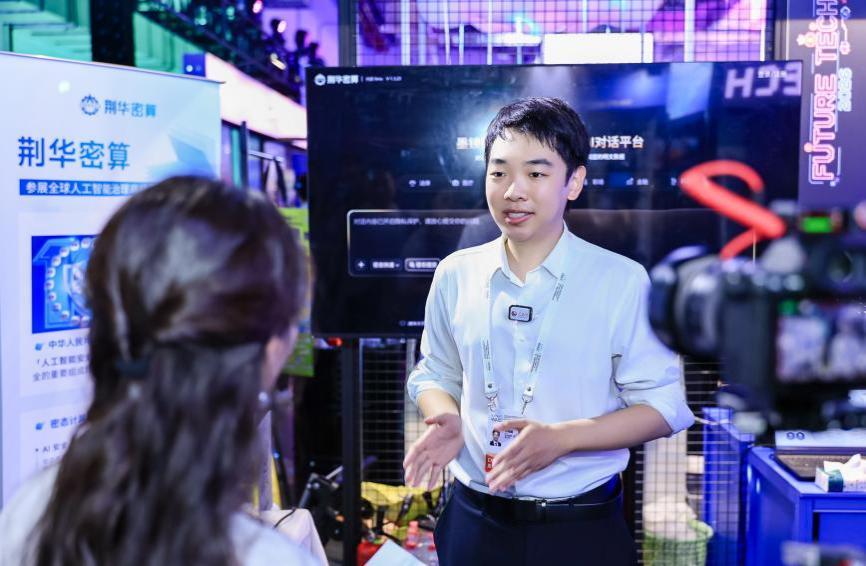
Behind this outstanding performance are the team's almost round-the-clock efforts over the past six months. Facing diversified business challenges, the team advanced simultaneously on the three fronts of R&D deepening, delivery and fulfillment and financing promotion. Through efficient collaboration, they jointly delivered the "Jinghua Speed" in the AI era.
Talking about this round of financing, Lin Xiuchun, Founder and CEO of Jinghua Privacy Computing, said: "Jinghua Privacy Computing has a very clear strategic goal. We aim to solve the problem that 'AI is not applicable' in high-sensitivity scenarios, and build privacy-preserving computing into a digital infrastructure that supports large-scale implementation in the large model and Agent era."
He believes that if the efficiency of ciphertext computing can be equal to that of plaintext computing, everyone will need data security and controllability.
Solving the "Dare to Use" Problem in the AI Industry Chain
If the first half of the AI competition focuses on the model capability of "whether it can be used", the key to winning the second half lies in whether enterprises and institutions dare to use the models and data.
The era of generative AI and Agent is triggering a paradigm shift in data leakage: 77% of global enterprise employees have uploaded sensitive data to public network AI, while agents can silently capture local private data for public network inference. Once private data is "remembered" by the model, it can never be withdrawn permanently, and data security risks are spreading rapidly.
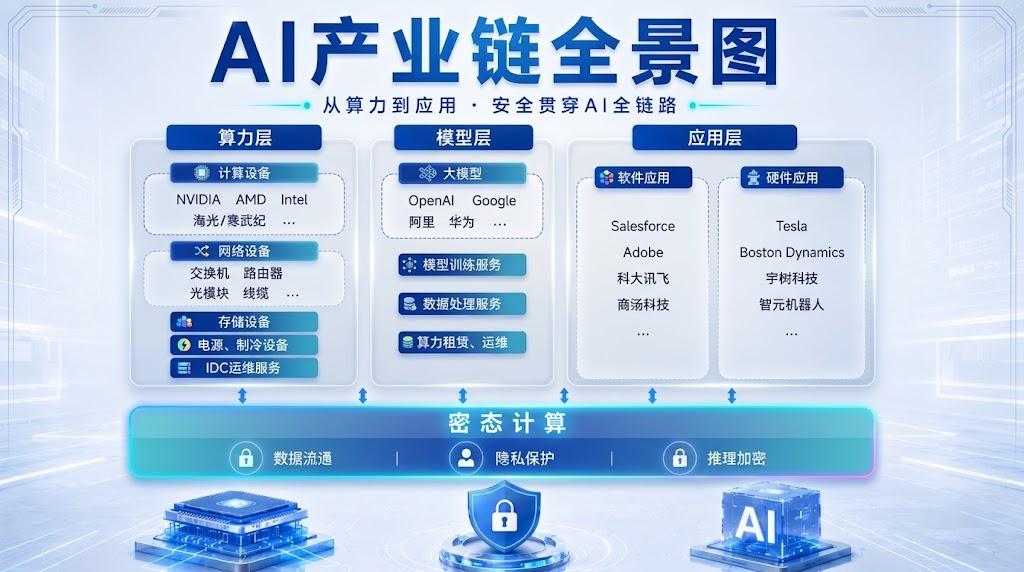
In sharp contrast, the AI industry chain itself has a huge volume. From the upstream computing power layer (NVIDIA, Broadcom, Hygon, Ascend, etc.), to the midstream model layer (OpenAI, Anthropic, Zhipu AI, etc.), and then to the downstream application layer (AI phones, embodied intelligence, autonomous driving, etc.), the total market value of the three tiers has exceeded 27 trillion US dollars.
However, the higher the value of the industrial chain, the greater the "hidden cost" of data that cannot safely enter the computing process: no matter how strong the computing power is, top hospitals dare not hand over medical records to large models for training; no matter how smart the model is, commercial banks dare not feed transaction data to public network risk control systems. Once trust is absent, industrial value cannot be truly released.
Claude overseas has recently been caught in a series of privacy and security scandals, as they publicly review a large number of files uploaded by users, which is in sharp contrast to their image of "security first". From user-shared dialogues being crawled by search engines to account sessions being targeted by malware, new incidents emerge almost every few weeks.
Facing this market pain point, why are large manufacturers with massive resources slow to penetrate into the privacy-preserving computing field?
Lin Xiuchun said frankly: "It's like asking people who make money by 'selling data' to lock up data. The profit foundation of traditional large manufacturers lies in obtaining user portraits and realizing data value, which is naturally opposed to thorough data privacy protection, and they lack the motivation to revolutionize their own business."
In addition, privacy-preserving computing faces a complex link where external hackers and internal risks are intertwined, with extremely complex engineering and extremely low fault tolerance. Once it is breached, it will directly shake the brand foundation of large manufacturers. The core is the structural dividend of neutrality -- the end point of data privacy security is "trust". Only independent third-party security vendors that do not participate in data monetization can truly build a full-link privacy-preserving infrastructure with no interest association and high credibility.
Lin Xiuchun believes: For large manufacturers, obtaining the dialogue records between users and AI can form more accurate user portraits for more precise advertising marketing, and the data can also be used to train the next generation of models to improve user experience. At this stage, whichever company takes the lead in promoting privacy-preserving computing is likely to fall behind in the main battlefield of model training, and lose a lot of commercial profits from high-quality marketing at the same time. This is a losing deal of "earning 100 but losing 1000".
Secondly, letting the subject that can benefit from it play the role of data protector is no different from "letting the weasel guard the chicken coop". Due to the objective internal drive in the economic structure, it will eventually only provide the most basic data protection for user privacy. Historically, no matter what industry, this role is usually played by a pure third party. Of course, no security solution can achieve 100% absolute security at present. For large model teams lacking relevant experience, attempts in the field of large model intelligent computing may damage the reputation of large manufacturers.
China's AI Security Should Not Be Constrained by Overseas Hardware
"Data is available but not visible" is a recognized solution to break through the industrial bottleneck, but the traditional privacy computing route is difficult to achieve real full-link encryption.
Jinghua Privacy Computing abandons the general computing route, focuses on AI intelligent computing, and re-engineers the cryptography route at the underlying layer.
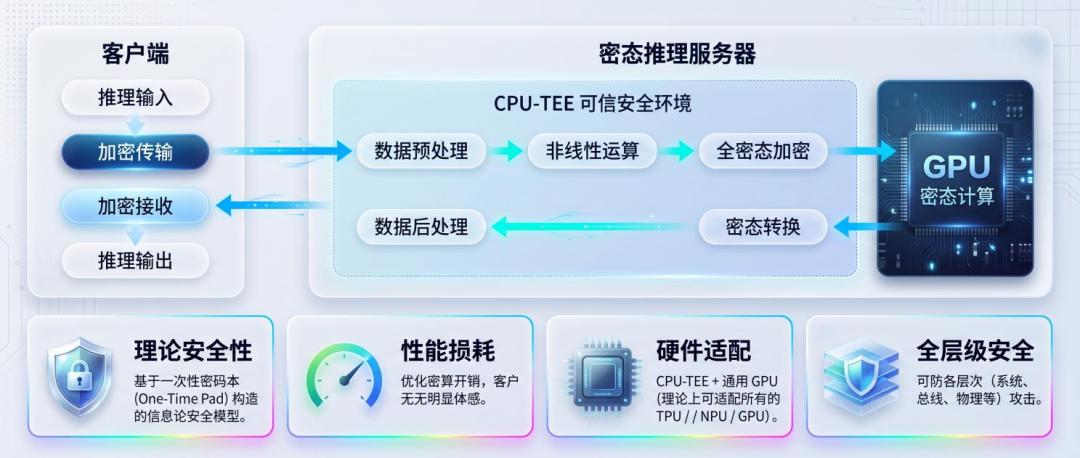
OPT Architecture
This engineering breakthrough successfully breaks the impossible triangle of "security, efficiency and generality" in privacy computing: in terms of efficiency, the loss is reduced to commercial level; in terms of generality, it gets rid of the dependence on overseas GPU-TEE, and is fully compatible with domestic computing power platforms such as Ascend and Hygon.
Lin Xiuchun said: "The encryption theory has existed for 20 years. The INFRA under encryption is the key. There are few teams in the world that specifically optimize the model computing efficiency for encrypted intelligent computing, but efficiency is the key for encryption technology to move from the exclusive use of a few units to universal application."
At present, based on this platform, Jinghua Privacy Computing has launched four products to the market: Trusted Token product that allows users to quickly obtain full-modal computing inference capabilities by calling the encrypted large model API; one-stop privacy-preserving agent development platform "Privacy MaaS"; China's first privacy-preserving AI dialogue platform "Sunglasses Bear"; and the whole-process decryption-free meeting recording system "Privacy Listen".
"Security never has 100% absolute guarantee. Without systematic large-scale product launch and red-blue confrontation, most of the time we don't even know where the problem is." Lin Xiuchun said, "Taking Jinghua Privacy Computing's privacy-preserving computing solution as an example, it has been deployed in 17 countries and regions with a multinational enterprise, serving nearly 100 million users. The performance and security problems encountered in this process allowed us to expose and solve key problems in advance."
As a result, "data is available but not visible" has changed from a cryptography problem to a deliverable and scalable engineering reality. The data security boundary of China's AI is no longer delineated by overseas hardware.
Full-stack Implementation and Insurance Coverage
"To make enterprises truly 'dare to use' AI, we cannot only rely on formulas and proofs, but also rely on actual combat in large-scale production environments." Lin Xiuchun said.
In a short period of time, Jinghua Privacy Computing officially released the "Privacy-preserving Large Model Infrastructure Platform", providing privacy-preserving operation space, multi-machine privacy interconnection, high-performance privacy-preserving computing, transparent privacy-preserving storage and continuous privacy-preserving security services, providing the industry with a low-threshold, high-trust large model privacy-preserving inference path.
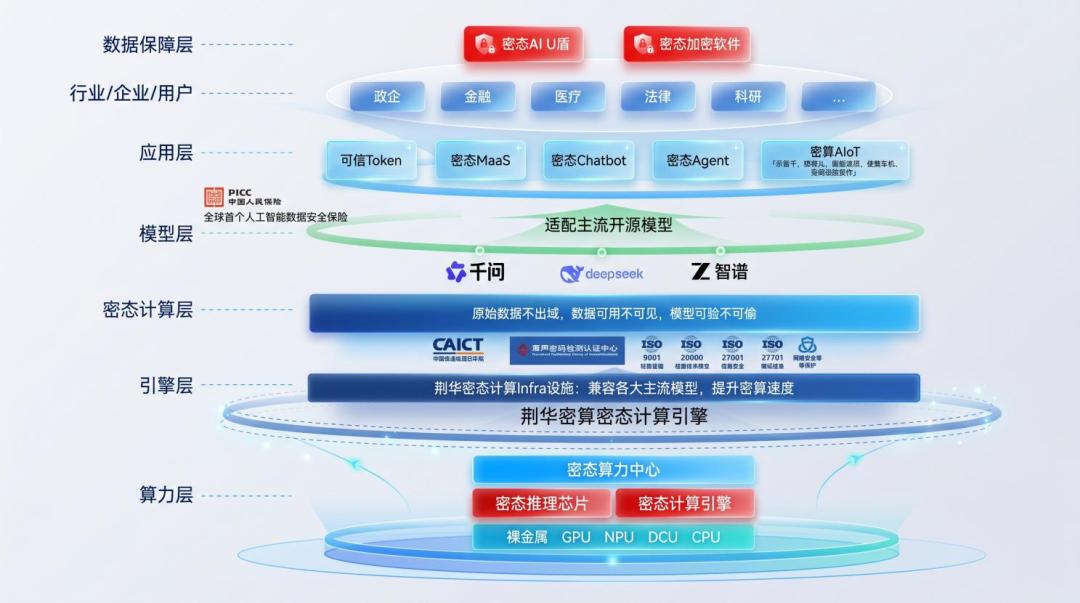
Full-link Privacy-preserving Computing Platform Architecture
Based on this platform, Jinghua Privacy Computing has quickly opened up a full-stack product array covering the development layer, application layer, terminal and data guarantee layer: Trusted Token that provides "zero-modification" access for API developers (the weekly Token consumption has exceeded 10 billion), low-threshold Privacy MaaS for government and enterprise customers, "Sunglasses Bear" for C-end full-process protection, and hardware-level high-privacy meeting system "Privacy Listen".
At present, Jinghua Privacy Computing has signed strategic cooperation frameworks with many computing power cloud vendors, and has completed access and cooperation of some products with a large cloud vendor. The key to providing encrypted cloud services is to achieve full-link security and efficient collaboration from the underlying layer to the application layer. Lin Xiuchun judges that encrypted cloud services will be a larger battlefield than encrypted SaaS in the future, which will bring more obvious revenue growth.
At the same time, in order to promote security from "self-certification" to "third-party institutional guarantee", Jinghua Privacy Computing took the initiative to contact many insurance companies, disclosed the core confidential scenarios to the insurance companies for investigation, and finally Jinghua Privacy Computing cooperated with The People's Insurance Company of China to pioneer the world's first AI data insurance. This first "AI dialogue product privacy protection network data damage compensation liability insurance" in China has a compensation limit of 2 million yuan. This not only means a breakthrough at the technical level, but also means providing customers with a full-link trust guarantee of "dare to use, dare to compensate".
Lin Xiuchun pointed out: "For privacy-preserving AI that is delivered to ToB and requires insurance underwriting, pushing the platform to commercial implementation is an extremely challenging thing. We not only need to invest huge capital and time, but also need to go through a lot of actual combat tests and trial and error in real and complex business scenarios. But only by gnawing down this hardest bone can we truly release data value on the premise of security."
Nowadays, the 10-billion-level weekly Token consumption has confirmed that the market has entered an explosive period. Jinghua Privacy Computing will follow the route of "benchmark building, scenario implementation, privacy cloud ecosystem establishment", making privacy-preserving computing a standard configuration in the AI era.
Zhongguancun Science City said: "With the popularization of large models, there have been many typical cases of information leakage caused by illegal use of AI tools. Jinghua Privacy Computing originated from Tsinghua University, rooted in Zhongguancun Science City, uses cryptography to reconstruct the underlying layer of AI computing, and pushes privacy-preserving computing from 'theoretically feasible' to 'commercially available' without relying on overseas hardware, providing trusted infrastructure for the implementation of large AI models in high-sensitivity scenarios, solving the problem of 'data dare not flow and dare not go to the cloud' in the era of large models and agents, and realizing that data is 'available but not visible' in the whole process of transmission, storage, inference and training. Zhongguancun Science City will continue to help Jinghua Privacy Computing grow into an infrastructure provider supporting the safe development of China's AI industry."
Northern Venture Capital said: "The higher the penetration rate of AI, the more prominent the value of the data security base. Jinghua Privacy Computing not only makes 'available but not visible' have the conditions for large-scale commercial use for the first time, but also reconstructs the trust standard of the industry by introducing a financial-level underwriting mechanism. With 100,000 levels of user demand verification, as well as ecological layout covering dozens of industrial partners and multiple high-value tracks, Jinghua Privacy Computing has taken the lead in crossing the commercial inflection point. We firmly believe that Jinghua Privacy Computing will become a key security infrastructure that promotes the full explosion of the large model industry."
Inno Tech Fund said: "With the increase of the penetration rate of large models in work and life, large models themselves are becoming a possible link of privacy leakage, which may also cause the public's trust crisis in large models. Therefore, the whole-process encryption of models will inevitably become a rigid demand gradually. Jinghua Privacy Computing makes 'security' and 'availability' hold true at the same time for the first time, and has adapted to most domestic models and chips. Inno believes that large model privacy will become an important topic, and we will continue to increase investment to support Jinghua, and believe that Jinghua can become a global leading model privacy protector."
SJ Capital said: "As AI moves from model capability competition to large-scale application, Token factories are becoming a new generation of AI infrastructure. In the next stage, Token factories should not only solve the 'production efficiency' problem, but also solve the 'trusted production' problem. Jinghua Privacy Computing is building a trusted Token factory for core enterprise businesses, connecting high-performance privacy-preserving computing with model services, so that sensitive data can continuously participate in inference within the security boundary and realize large-scale supply by Token. Trusted Token is expected to become an important part of AI infrastructure. Relying on independent privacy-preserving computing technology, Jinghua is building a trusted ecosystem covering computing power, models, applications and industrial partners."
When large AI models fully move from "technical trial" to "core business penetration", trusted and secure computing power supply will become a precondition for industrial explosion.
Standing at the new starting point of the nearly 100 million yuan Pre-A round of financing, Jinghua Privacy Computing, based on the independent and controllable privacy-preserving intelligent computing platform, will continue to break through the trust depression together with investment institutions, industrial giants and ecological partners, so that every inference of AI runs on the foundation of security and trust.