The enterprise accused of stealing and transmitting code has issued a letter to pursue accountability, and Zhipu announced that ZCode will be open-sourced and subject to third-party audit.
On September 21, Zhipu (2513.HK), known as the "first large model stock" on the Hong Kong Stock Exchange, told Jiemian News that its AI programming tool ZCode is about to be officially open-sourced, and has invited the China Academy of Information and Communications Technology and NSFOCUS to conduct security audits. This is Zhipu's third public response to the data privacy controversy, following its first apology on September 18 and the launch of a patched version on September 19.
Zhipu revealed that it has invited two authoritative third-party institutions, the China Academy of Information and Communications Technology and NSFOCUS, to complete the first round of verification. The technical evaluation by the China Academy of Information and Communications Technology confirmed that the involved zcode-prod Alibaba Cloud OSS bucket currently has zero data on the cloud; the review results from NSFOCUS show that all data objects in the bucket and the bucket itself have been deleted, the updated ZCode v3.14.0 client has completed full rectification, the Repo Wiki entry and the corresponding generation link have been removed, and no functional paths that can trigger local repository snapshots or file exfiltration have been found.
Zhipu also stated that this open source move is the first step to address public concerns about ZCode's data processing; it will later establish a regular security operation mechanism, publish code security audit reports on a monthly basis, and set up a public product security vulnerability reporting mechanism to promote the product to move more thoroughly towards community governance, allowing developers to freely download and inspect the core code, and jointly participate in the improvement of product security and functions.
This public controversy was first publicly disclosed by tech blogger ferstar on his personal blog on September 18. While cleaning up his local disk, he accidentally found that the ZCode desktop client under Zhipu would automatically package, encrypt and upload the code of the entire workspace to the Alibaba Cloud OSS storage service when the user was logged in. According to the reverse analysis results, the content packaged and uploaded not only included the source code of the current project, but also the complete Git version history, LFS large file cache, reflog records and some global development configuration files, covering almost all the core R&D assets of the project.
What further dissatisfied the developer community is that this upload mechanism is enabled by default, and users cannot find the corresponding off switch in the client settings interface; in addition, the RSA public key used for encryption is dynamically issued by the server, and the private key is only stored on the cloud, so users themselves cannot decrypt the encrypted data packets generated locally. This disclosure quickly spread in the tech circle, many enterprise users began to worry about the security risks of their own code assets and trade secrets, and even some developers temporarily disabled related tools to investigate the possibility of data leakage.
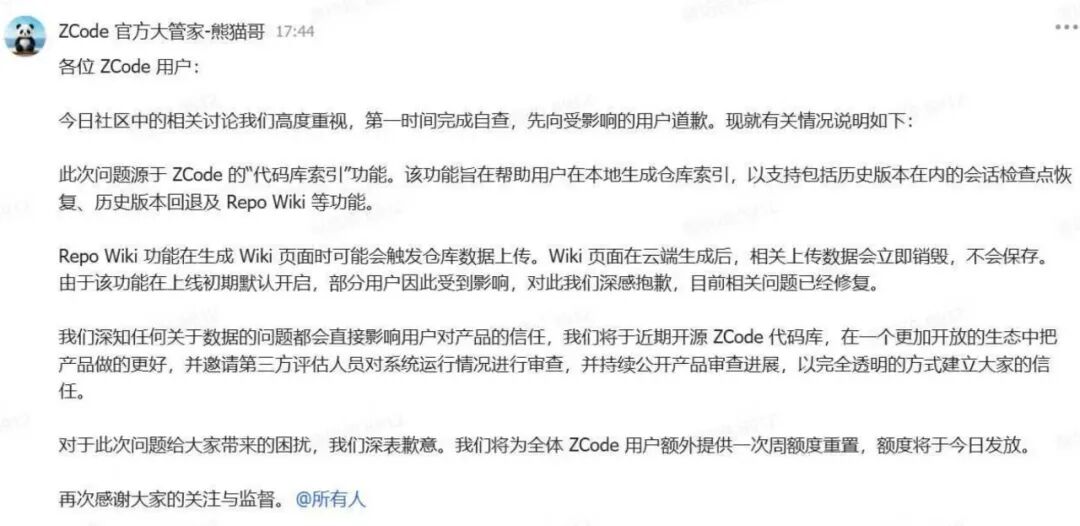
Apology statement released in ZCode's official user group
That same evening, Zhipu released an apology statement in ZCode's official user group, making its first official explanation of the incident. Zhipu stated that the data upload behavior originated from the built-in "codebase indexing" function of the product, which is designed to support features such as historical version rollback, session checkpoint recovery, and RepoWiki code knowledge base generation, where the RepoWiki function triggers repository data upload when generating pages on the cloud.
Zhipu emphasized that all uploaded data is only used to generate Wiki pages and will be destroyed immediately after completion, and will not be retained on the cloud. In response to the problem that the function was enabled by default and could not be turned off, Zhipu admitted that the function was not fully notified to users at the initial stage of launch, nor was a manual off entry provided, and the technical fix has been completed as soon as possible, with the relevant upload link removed. At the same time, Zhipu announced three initial remedial measures: open source the ZCode codebase, accept community supervision, invite professional third-party institutions to conduct security reviews of the system operation and announce the progress; and provide an additional weekly quota reset as compensation for all ZCode users.
The next day, ZCode pushed the v3.14.0 version, and the update log stated that it "fixed the abnormal upload issue of the repository wiki". However, the incident did not subside as a result. On September 19, Taiyuan Chengming Technology Co., Ltd. officially sent a letter to Beijing Zhipu Huazhang, requesting a written explanation on issues such as data deletion, private key custody and whether cross-border transmission had occurred, and reserved the rights to claim compensation and file a lawsuit.
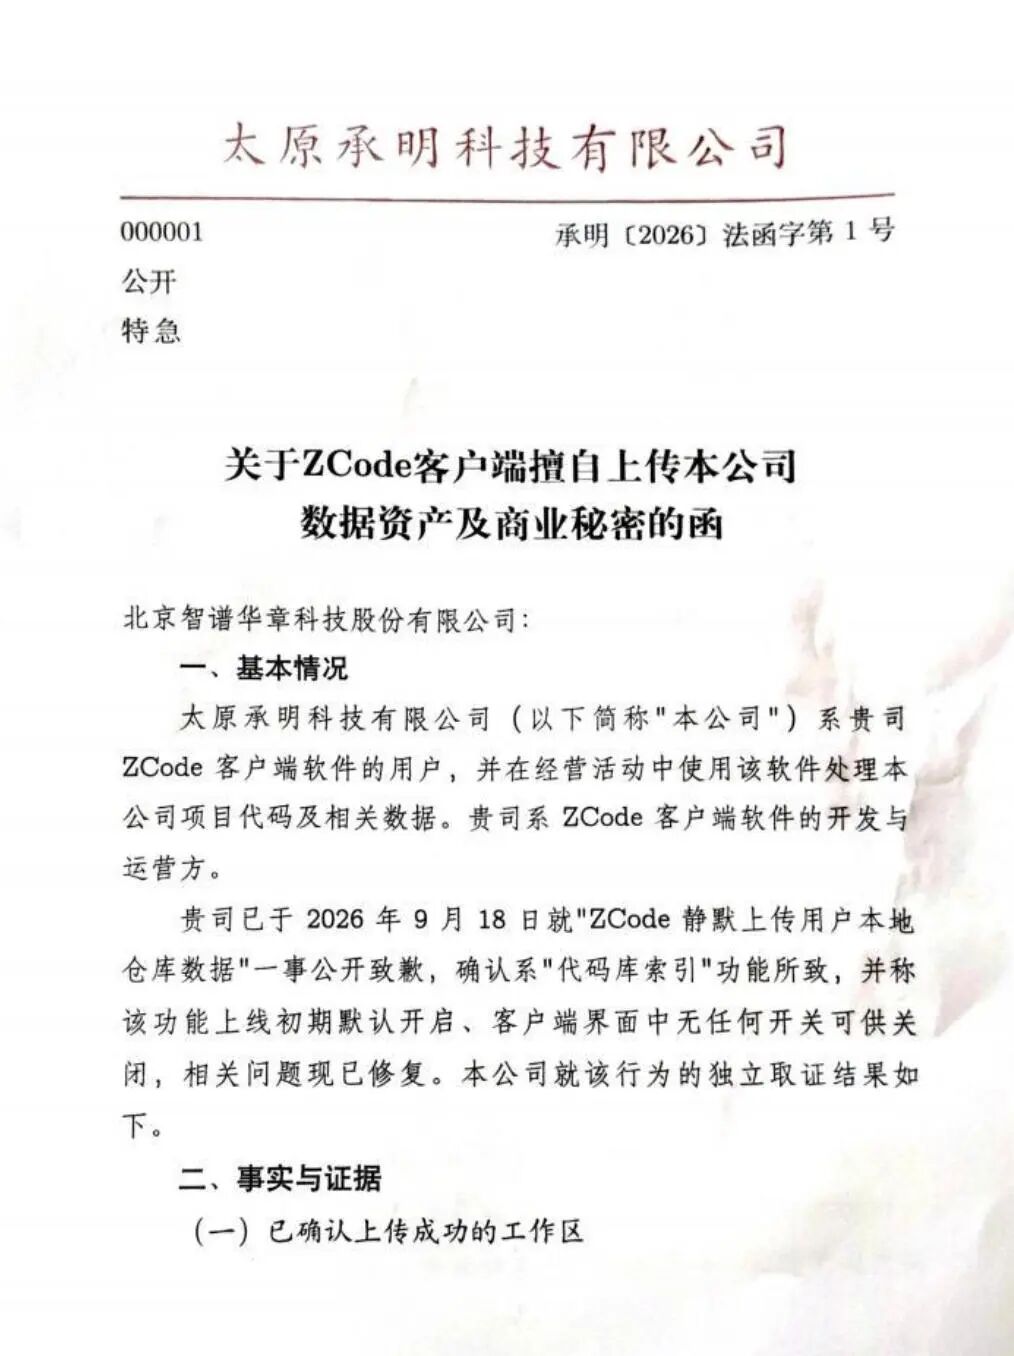
The letter from Chengming Technology
Chengming Technology stated that after independent evidence collection by the company's technical department, it was confirmed that ZCode's upload behavior was automatically triggered and occurred in batches, and the involved data was far more than ordinary "code snippets", but included complete archived files such as the full source code of the project, system architecture design, full version control history, database access passwords, cloud service permission credentials and employees' personal information, which significantly exceeded the collection scope specified in ZCode's Privacy Policy.
Chengming Technology proposed that although Zhipu claimed that the problem had been fixed on September 18, upload behavior was still detected in the early morning of that day, thus questioning the actual effect and thoroughness of the rectification. Chengming Technology put forward a total of 12 specific response requirements in the letter, including disclosing the complete list of data uploaded, providing the destruction certificates of all uploaded data, disclosing the qualifications and review scope of the third-party audit institutions, and providing a risk investigation plan for enterprise users, and explicitly stated that it reserves the right to take further legal action.
As a leading large model enterprise in China, Zhipu has recently completed a new round of financing, with its market valuation ranking at the forefront of the industry. ZCode is one of its core products for developer scenarios, and has accumulated a large number of individual and enterprise users since its launch with features such as full-project code understanding, intelligent completion, and debugging assistance. The data processing transparency of this client product that carries millions of developers' daily code assets is directly related to the foundation of Zhipu's reputation.
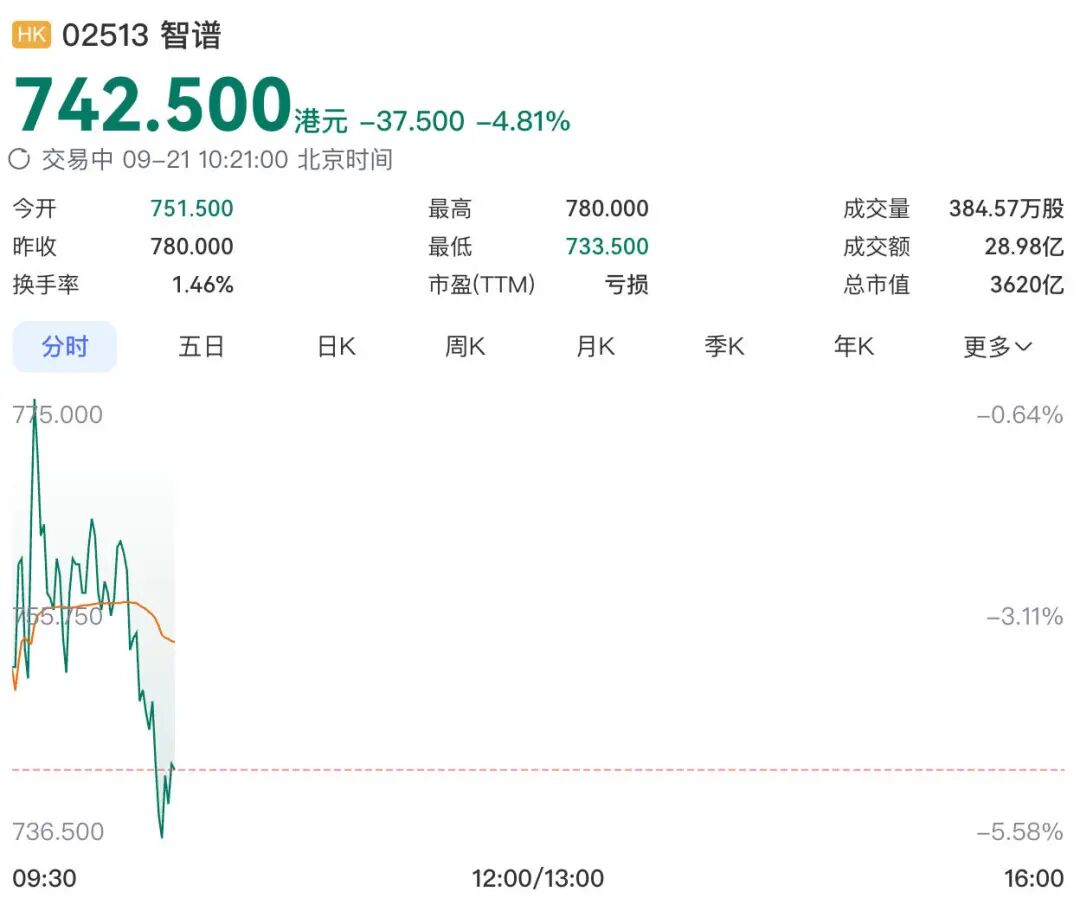
Affected by this incident, Zhipu's Hong Kong stock opened lower and moved lower today. As of press time, the company's share price fell by more than 4% at HK$742.5 per share, with a total market value of HK$362 billion.
This article is from the WeChat official account "Jiemian News", author: Li Kefeng, published with authorization by 36Kr.