GPT and Claude account balances were wiped out overnight, and OpenCode has blown up in a major crisis.
Waking up to a total disaster!
Today, a large number of OpenCode developers around the world have been hit by a massive theft.
In just a few hours, almost all the Tokens in their accounts were drained, and the entire AI industry was thrown into total panic.
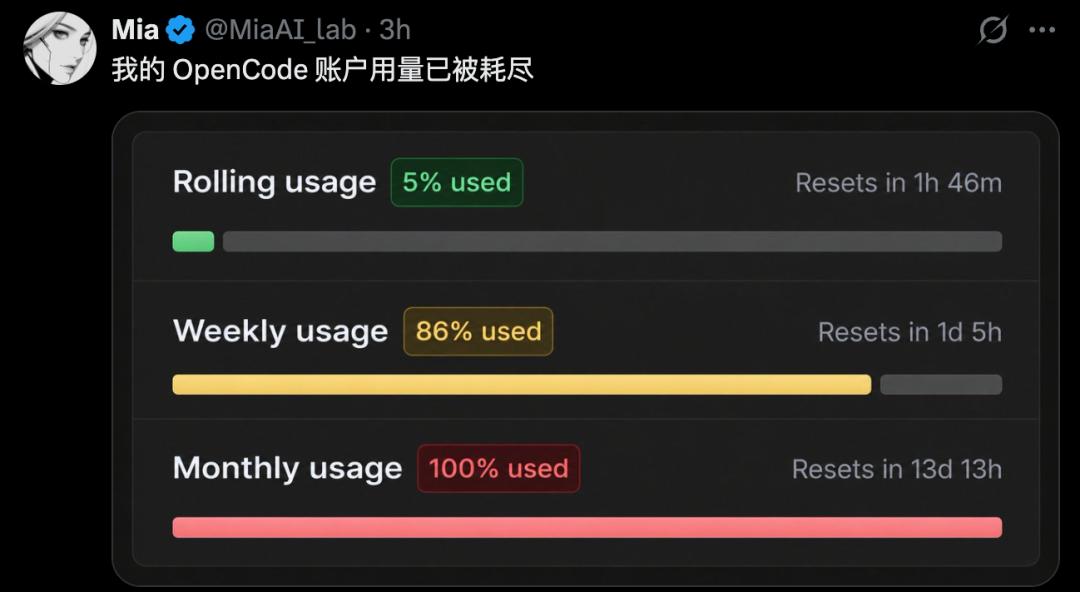
After the incident, OpenCode, the open-source AI programming tool, immediately launched an investigation and confirmed that this was a security vulnerability incident.
Approximately 1.4% of Console users were unfortunately affected this time.
The "big three" (OpenAI, Claude, Gemini) API Keys they stored in the workspace were completely exposed without any protection.
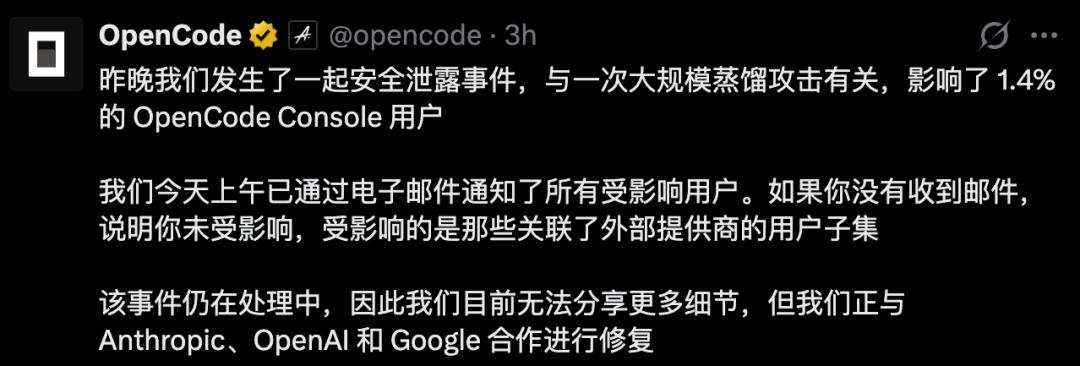
Hackers showed no mercy after obtaining the Keys, and immediately made massive API calls to top-tier large models.
One affected user shared their bill showing that their Anthropic account was charged 400 US dollars in the blink of an eye; an even worse hit user had over 1700 US dollars stolen directly through unauthorized calls.
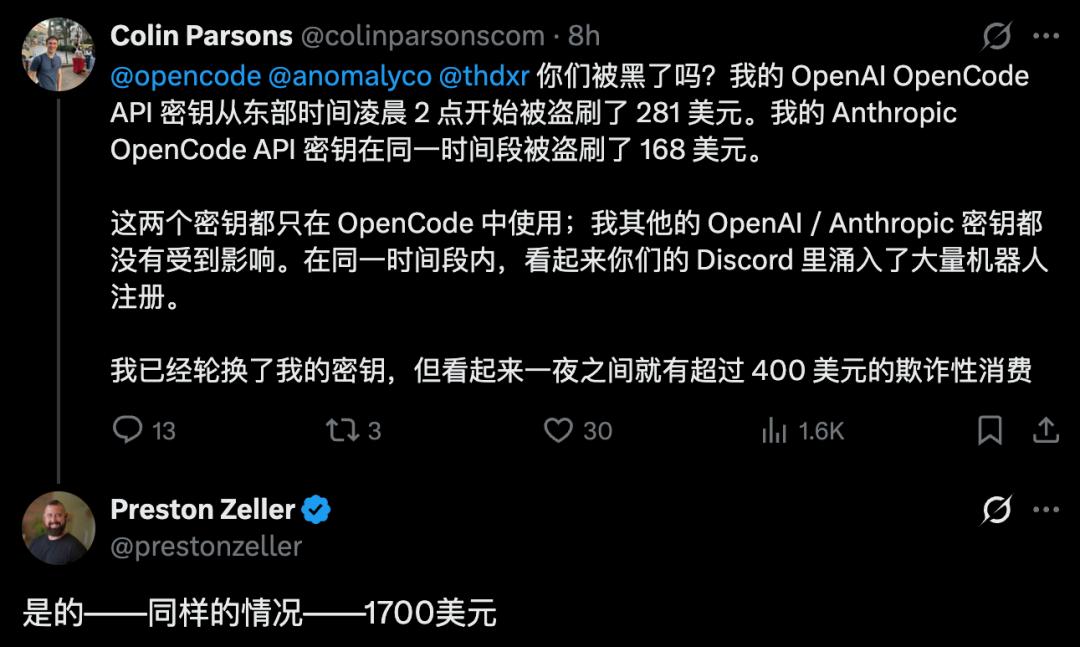
OpenCode has sent warning emails to developers overnight, stating that it is working together with Anthropic, OpenAI and Google to "put out the fire".
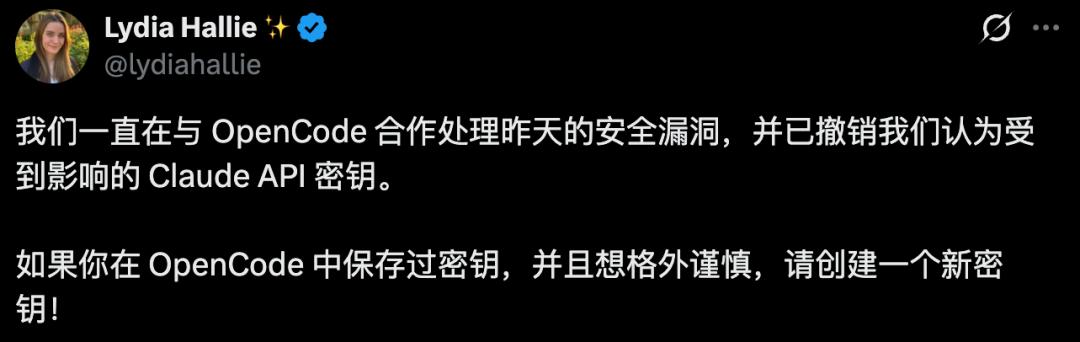
Lydia Hallie, head of Anthropic, also responded quickly: "All suspected leaked Claude API keys have been forcibly revoked at present".
Shocking Vulnerability Exposed on OpenCode
Over $1700 Stolen via Unauthorized API Calls Overnight
The whole incident of OpenCode being looted spread extremely fast.
At the very beginning, only a few programmers sporadically shared their absurd API bills —
After a night of sleep, the Token usage in the background skyrocketed like a rocket, directly draining the account balance to zero, and even triggering automatic top-up.
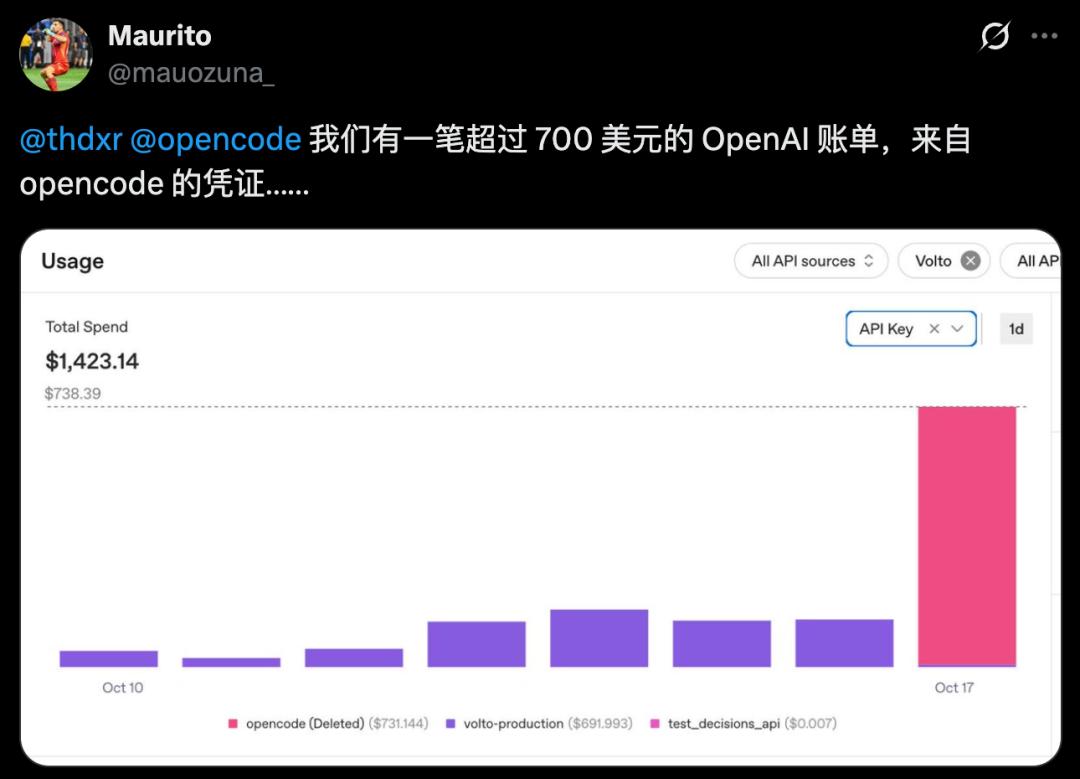
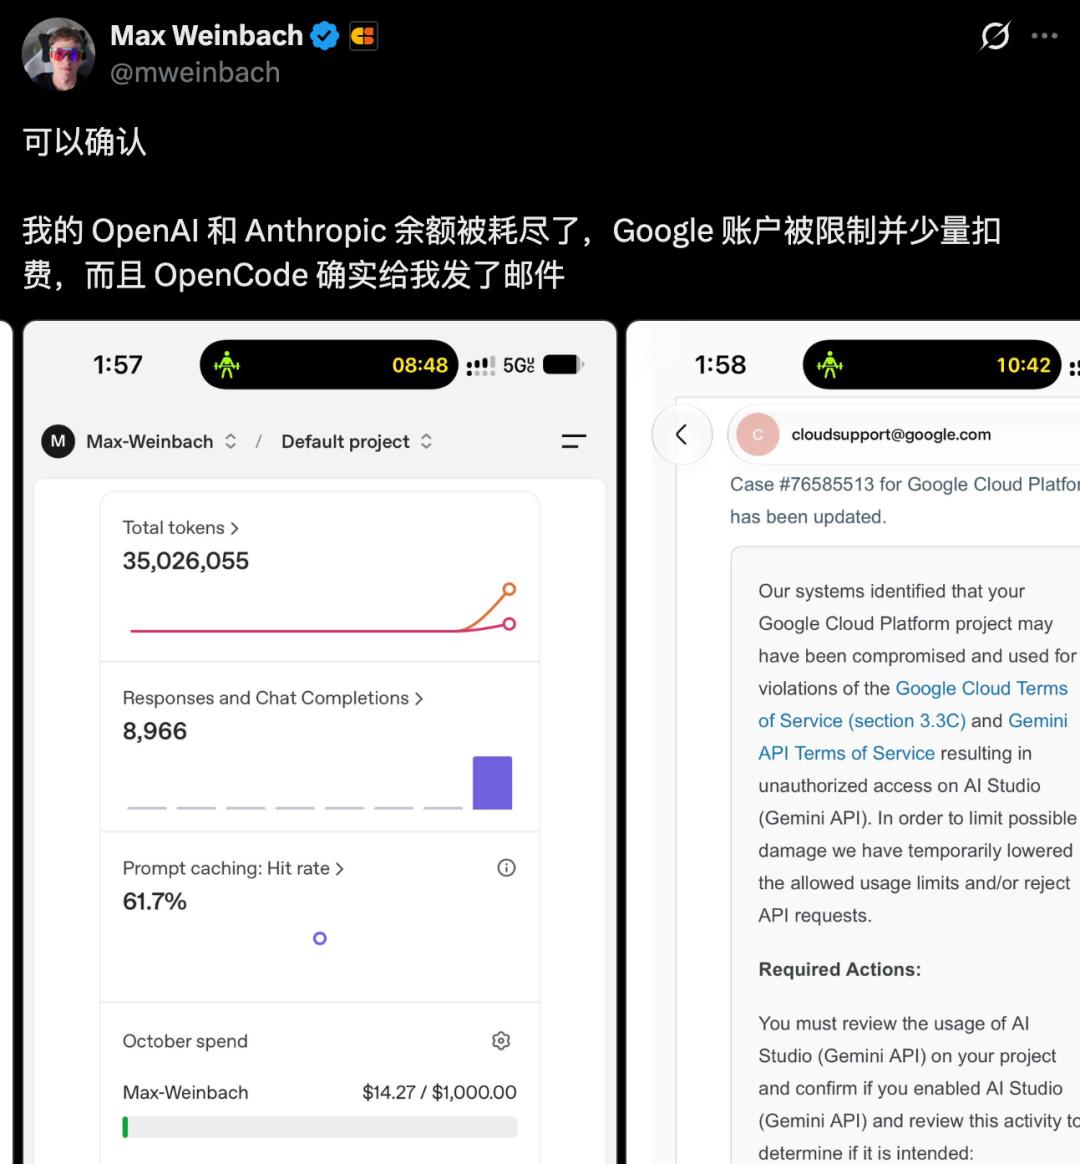
Shortly after, someone posted a screenshot showing that their Anthropic account was charged $400 without their knowledge.
Worse still, some people even had their Google Cloud API bills surge to an extremely high level, incurring an unexplained sky-high deduction of more than $1000.
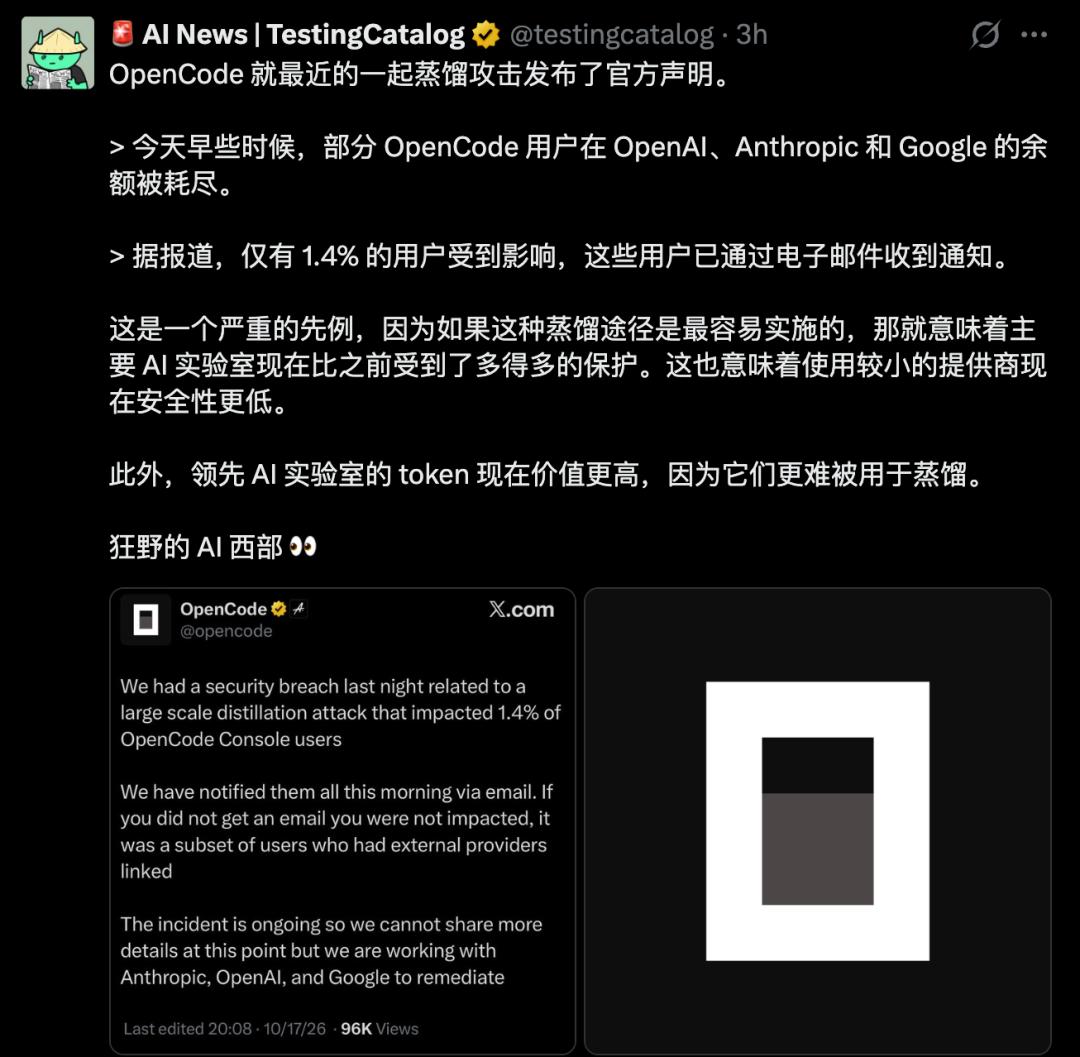
As the incident escalated, the OpenCode official account posted on X urgently, confirming the worst suspicion that everyone had —
Last night, we suffered a security vulnerability related to a large-scale distillation attack, which affected 1.4% of OpenCode Console users.
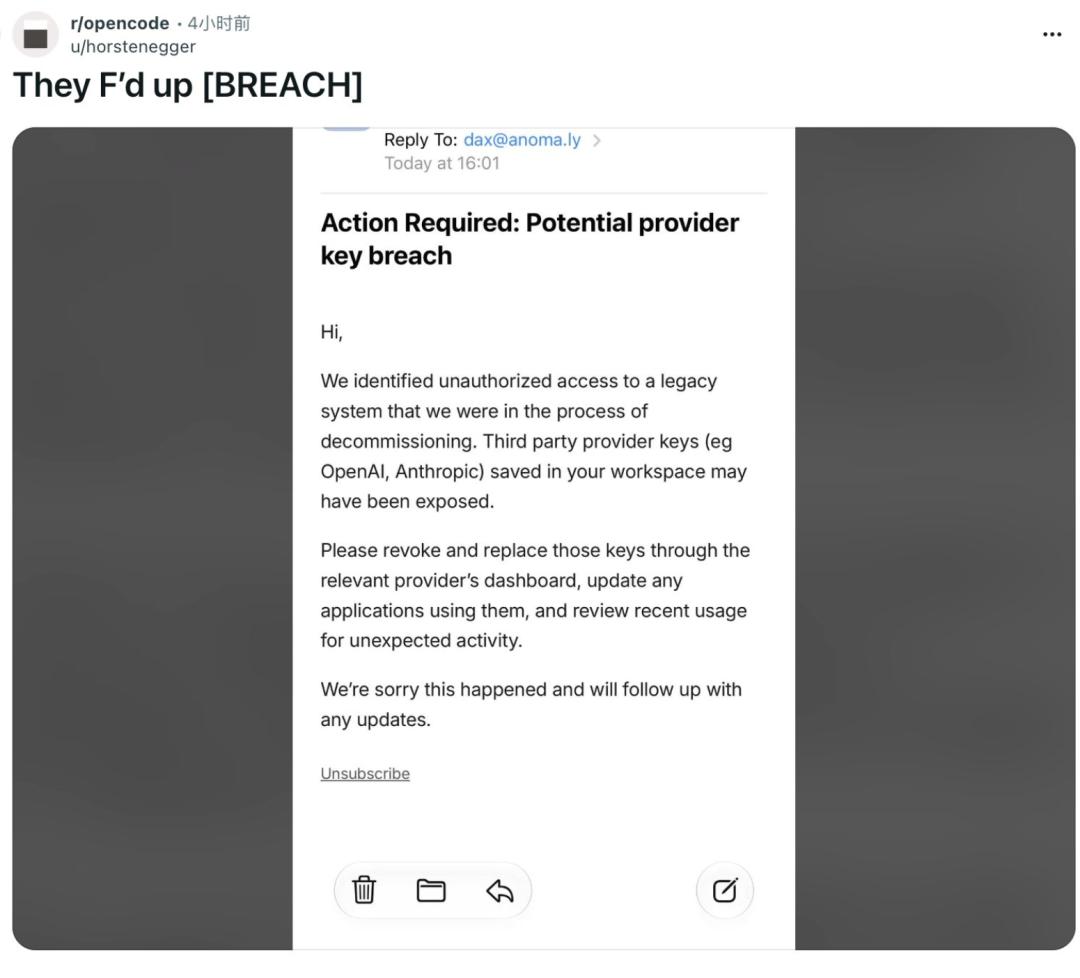
In the urgent email sent to users, OpenCode finally made the full disclosure:
The old legacy system that was about to be decommissioned caused this major incident.
Even the Founder Was Not Spared
The official investigation found that this system, which had not been shut down in time, was completely compromised by hackers.
All third-party service provider API keys stored in the workspace, including those of OpenAI, Anthropic and others, may have been exposed.
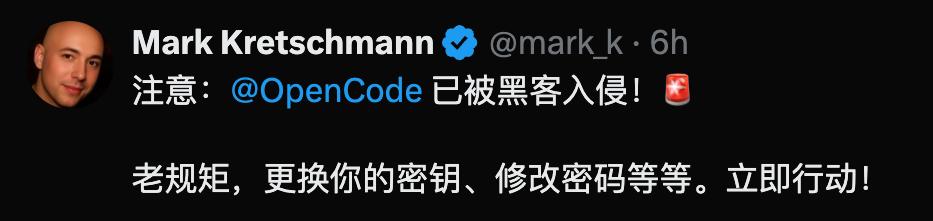
At the moment, OpenCode is urging users to take immediate self-rescue measures: revoke and reconfigure the Keys immediately, update application settings, and carefully check all recent call bills.
The most ironic thing is that in this hacker attack that spread across the entire network, even the founder of OpenCode was not spared.
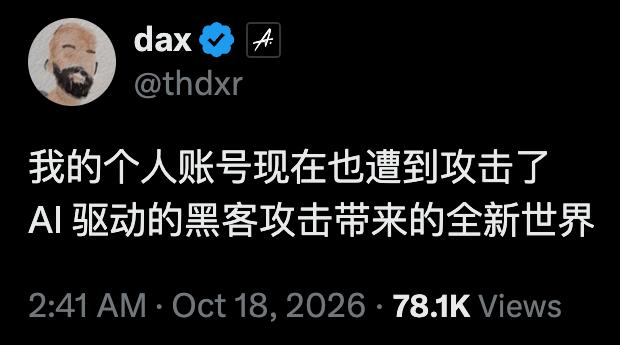
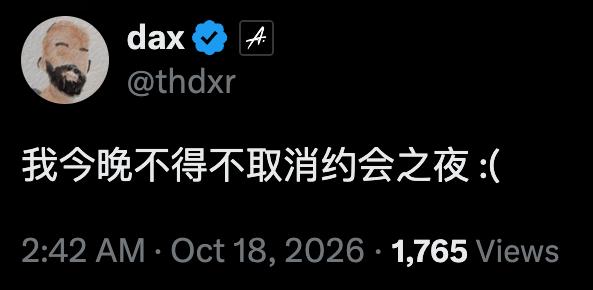
Shortly after the official statement was released, Dax Raad, co-founder of OpenCode, posted on X, full of helplessness and shock:
Even my own personal account is under attack right now. This wave of AI automated hacker attacks has truly opened up a whole new world.
Hackers Are Stealing Free API Access to Train Their Own Models
What is more dramatic is that the hackers did not steal the keys for resale, nor to steal personal chat records.
They used the Tokens to "train their own models".
These hackers targeting OpenCode converted every penny of the quota in these Keys into high-quality Tokens from top large models within a window of just a few hours.
To make a small model perform well, the most core fuel is a massive amount of high-quality Chain-of-Thought and code generation data.
If you directly purchase APIs from OpenAI and Claude to generate such training data, it will easily cost millions or even tens of millions of dollars.
Moreover, all major AI giants have long prohibited using the output of their own models for training in their terms of service, and have deployed extremely strict risk control systems in the background.
As a result, the hackers came up with an extremely malicious trick of "killing two birds with one stone", scamming developers to get free distributed API access.
By compromising third-party AI tool aggregation platforms like OpenCode, hackers obtained thousands of real developers' API Keys at one go.
During the whole process, every token consumption is charged to the account of the affected developer.
AI industry insider TestingCatalog pointed out sharply that this sets an extremely dangerous precedent! This means that using small and medium-sized third-party service providers has become more dangerous than ever before.
Don't Just Change Your Password!
If Old Keys Are Not Revoked, Your Money May Keep Being Wasted
For those who received the OpenCode security email, the most important action to take right now is clearly stated in the notification:
Go to the official console of the corresponding model service provider to revoke and replace any API keys that may have been leaked.
Changing your login password cannot replace revoking your API keys.
Deleting the configuration only in OpenCode or closing the local program cannot automatically invalidate the already leaked credentials. You must go to the platform that issued the keys to invalidate the old Keys.
Then check your recent usage and bills, keep the abnormal call records, consumption time and related notifications, and apply to the service provider for investigation and fee processing.
Normal applications that rely on the old keys also need to be updated synchronously.
This OpenCode leak exposed the keys of 1.4% of its users. The proportion is not large, but the lesson is huge:
In the AI era, API keys are the second ID of developers.
Never hand it over casually to any "convenient" console. After all, hackers will never feel bad for your bills.
References:
https://x.com/opencode/status/2111519637049319818?s=20
This article is from the WeChat official account AI Era, Author: ASI Revelation, Editor: Taozi, published with authorization from 36Kr.